HIPAA vs SOC 2: Do You Need Both for Your Health-Tech Product? (2026)
HIPAA vs SOC 2: Do You Need Both for Your Health-Tech Product? HIPAA vs SOC 2 Health-tech founders usually hit this question the moment a
HIPAA vs SOC 2: Do You Need Both for Your Health-Tech Product? HIPAA vs SOC 2 Health-tech founders usually hit this question the moment a
HIPAA Compliance Checklist for Digital Health Startups Hipaa compliance checklist isn’t a certificate you earn once and file away — it’s an ongoing set of
PCI DSS Levels Explained: Which Level Applies to Your Business PCI DSS Levels : Every business that touches cardholder data gets sorted into a PCI
PCI DSS v4.0 Compliance Checklist for SaaS & Fintech Companies Getting PCI DSS compliance checklist isn’t a single event — it’s a sequence of well-defined
PCI DSS v4.0 requirements What’s New and Who Needs to Comply PCI DSS v4.0 requirements stopped being “something to plan for” a while back — if
ISO 27001:2022 Annex A Controls Explained (All 93 Controls) ISO 27001:2022 Annex A Controls is where every ISO 27001:2022 project eventually lands. It’s the 93-control catalogue
ISO 27001:2022 Certification Process: Step-by-Step Guide Getting ISO 27001:2022 certified isn’t a single event — it’s a sequence of well-defined phases, each building on the
ISO 27001:2022 changes What Changed From the 2013 Version ISO 27001:2022 changes eventually ran into the same question: what actually changed in the 2022 update, and
SOC 2 Bridge Letters: What They Are and When You Need One SOC 2 Bridge Letters has an expiration problem built into it: it only covers
SOC 2 report enterprise buyers : What Enterprise Buyers Expect to See Getting a SOC 2 report enterprise buyers is only half the job. The
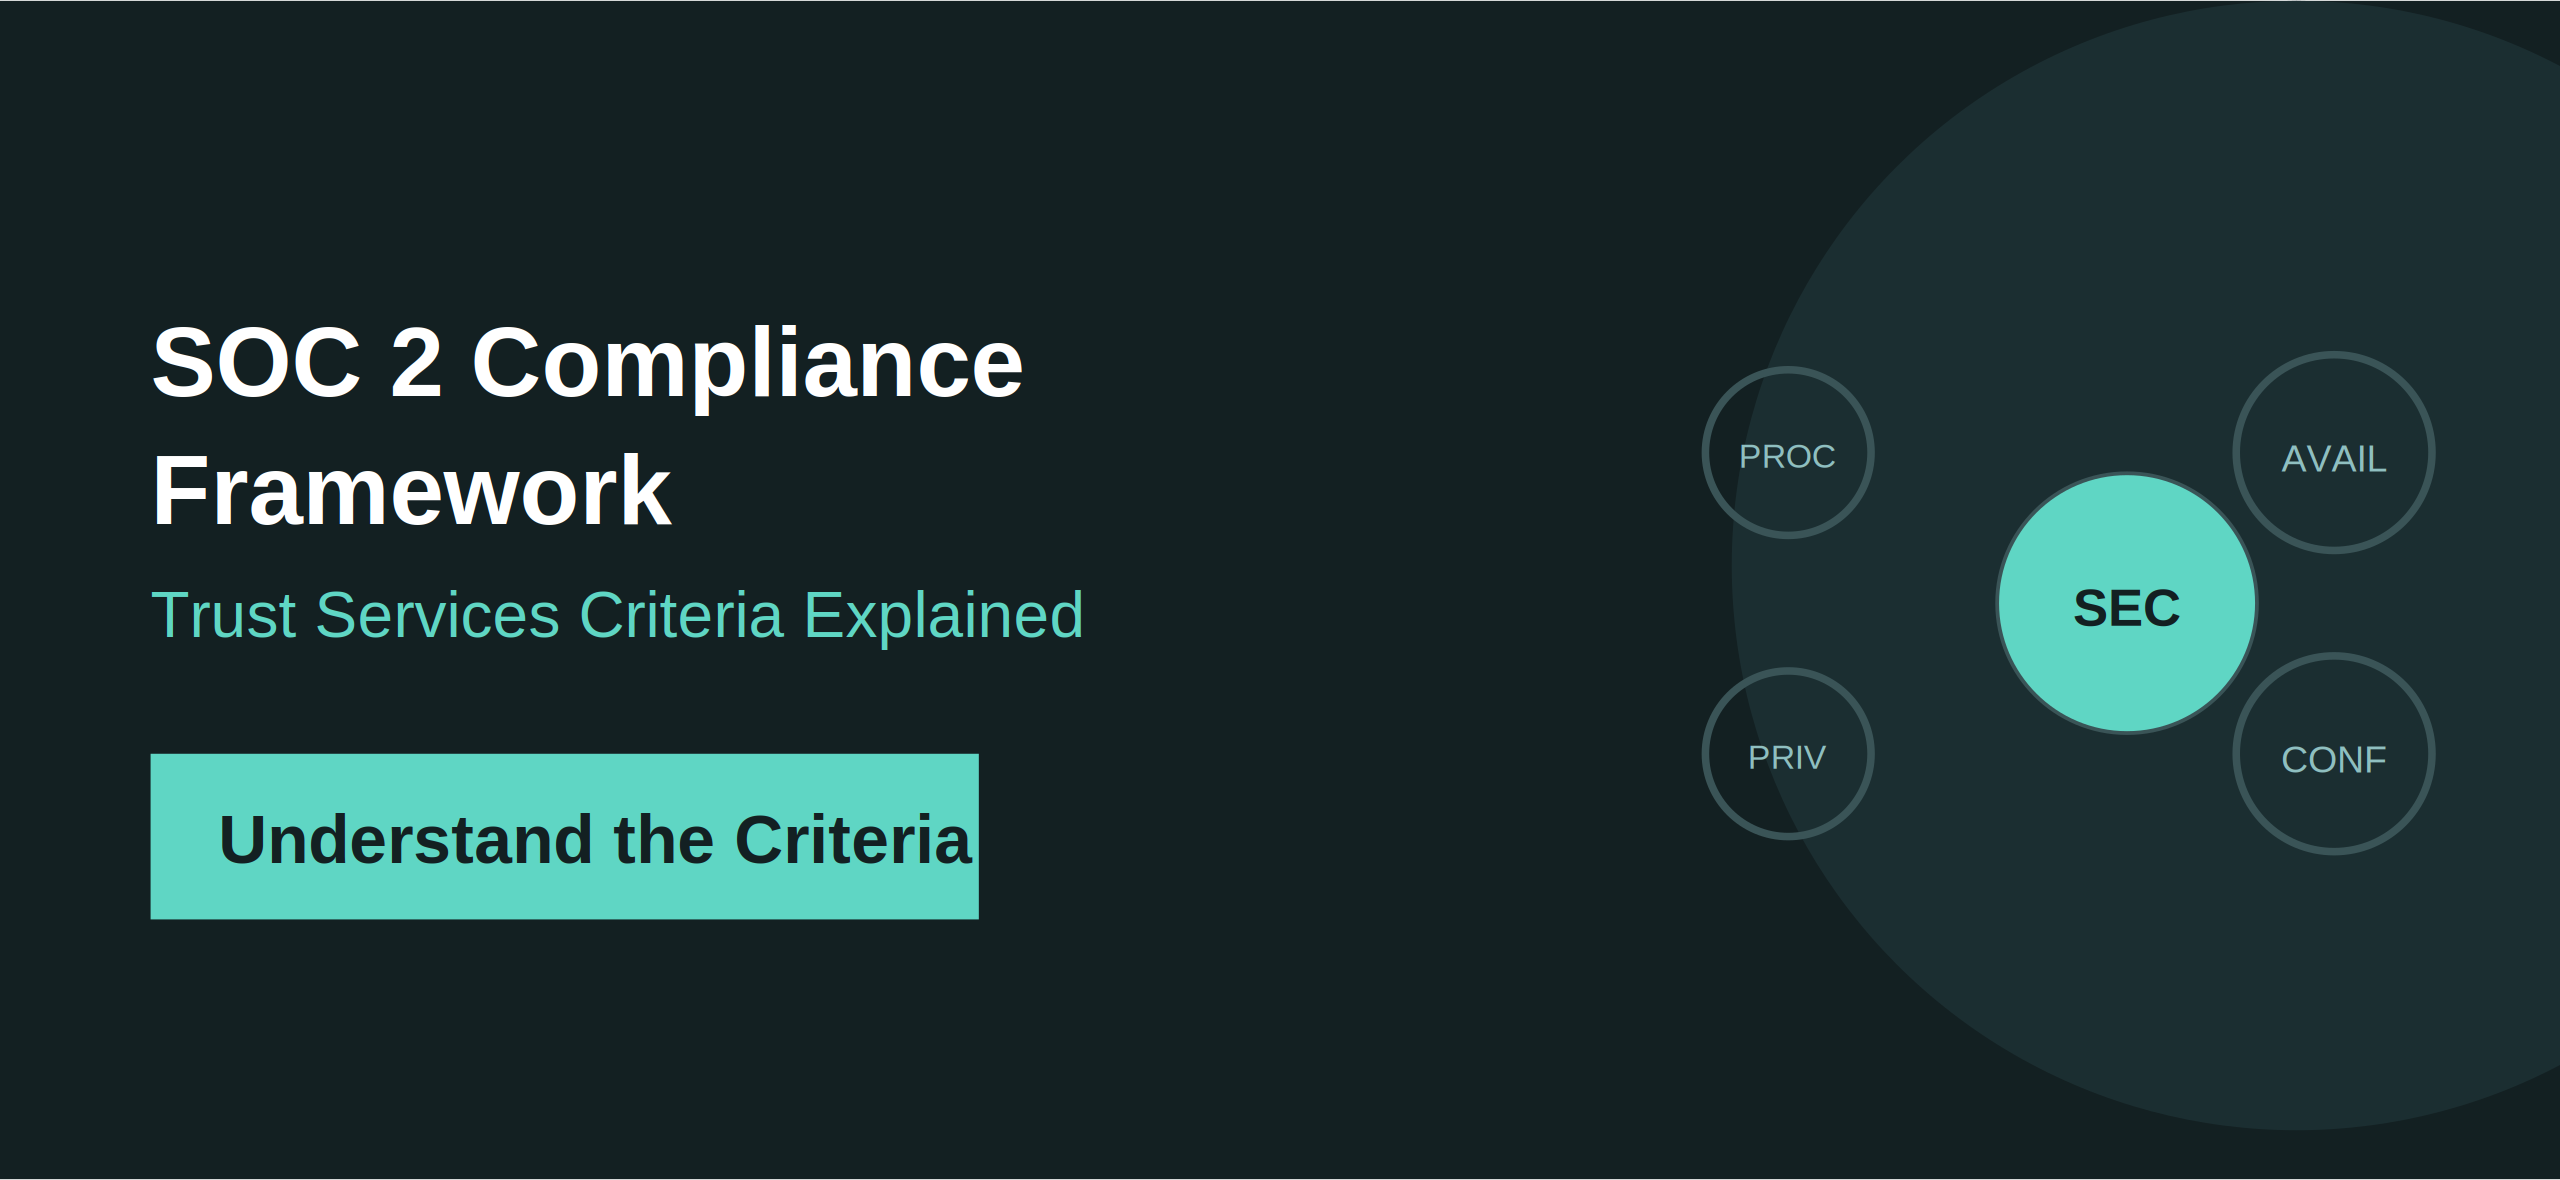
SOC 2 Compliance Framework: Trust Services Criteria Explained Every SOC 2 Compliance — Type I or Type II — is built on five criteria defined